Six tabs: General, Security, Resources, Licence, Remote and Audit.
General
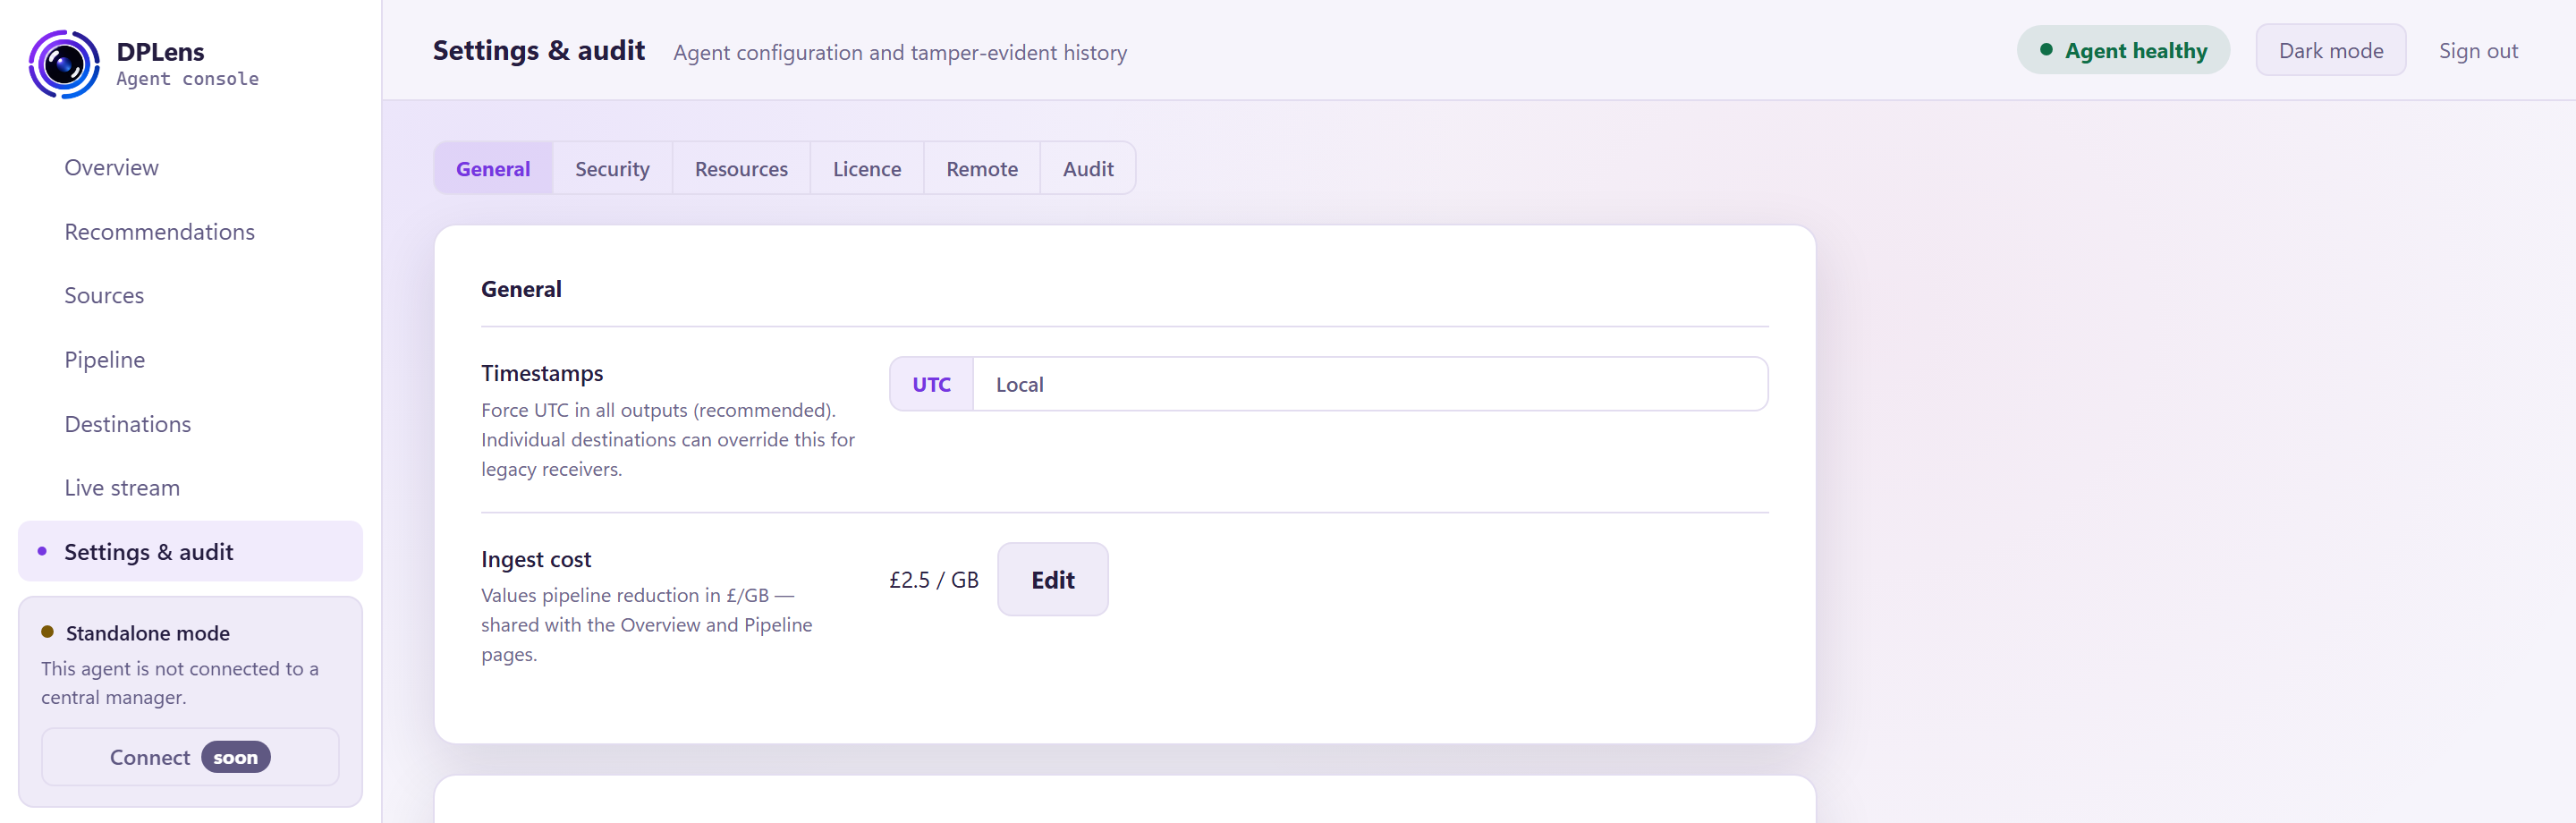
Timestamps
UTC (recommended) or Local.
Timestamps are normalised to UTC as soon as an event is collected and stay in UTC inside DPLens. This setting controls how they are written out. Individual destinations can override it for a receiver that insists on local time.
Ingest cost
What a gigabyte of ingest costs you, in pounds. It is used to show what your filtering saves, on Overview and Pipeline.
Setting it honestly is worth doing: it turns "we dropped 40% of events" into a number you can take to a budget conversation.
Console access
| Setting | What it does |
|---|---|
| Console | On or off. Off means no console process runs at all. |
| Console port | Which port to serve on. Minimum 1024. |
| Remote access | Off by default — the console listens on localhost only. |
| Allowed networks | Addresses or CIDR ranges that may reach the console, one per line. Required before remote access can be turned on. Loopback is always allowed. |
| Listen address | Where the console is actually served, as it stands now. |
| Your address | The address this browser session came from, and whether it is loopback. |
| Refused connections | How many connections have been turned away by the allow-list. |
| TLS certificate | Which certificate the console is using. |
Allowed networks are checked before the TLS handshake, so a machine outside the list never gets as far as negotiating.
Switching the console off is a one-way trip from the console's point of view: turning it back on means editing the configuration file and restarting the service, because there is no web interface running to do it from.
Security
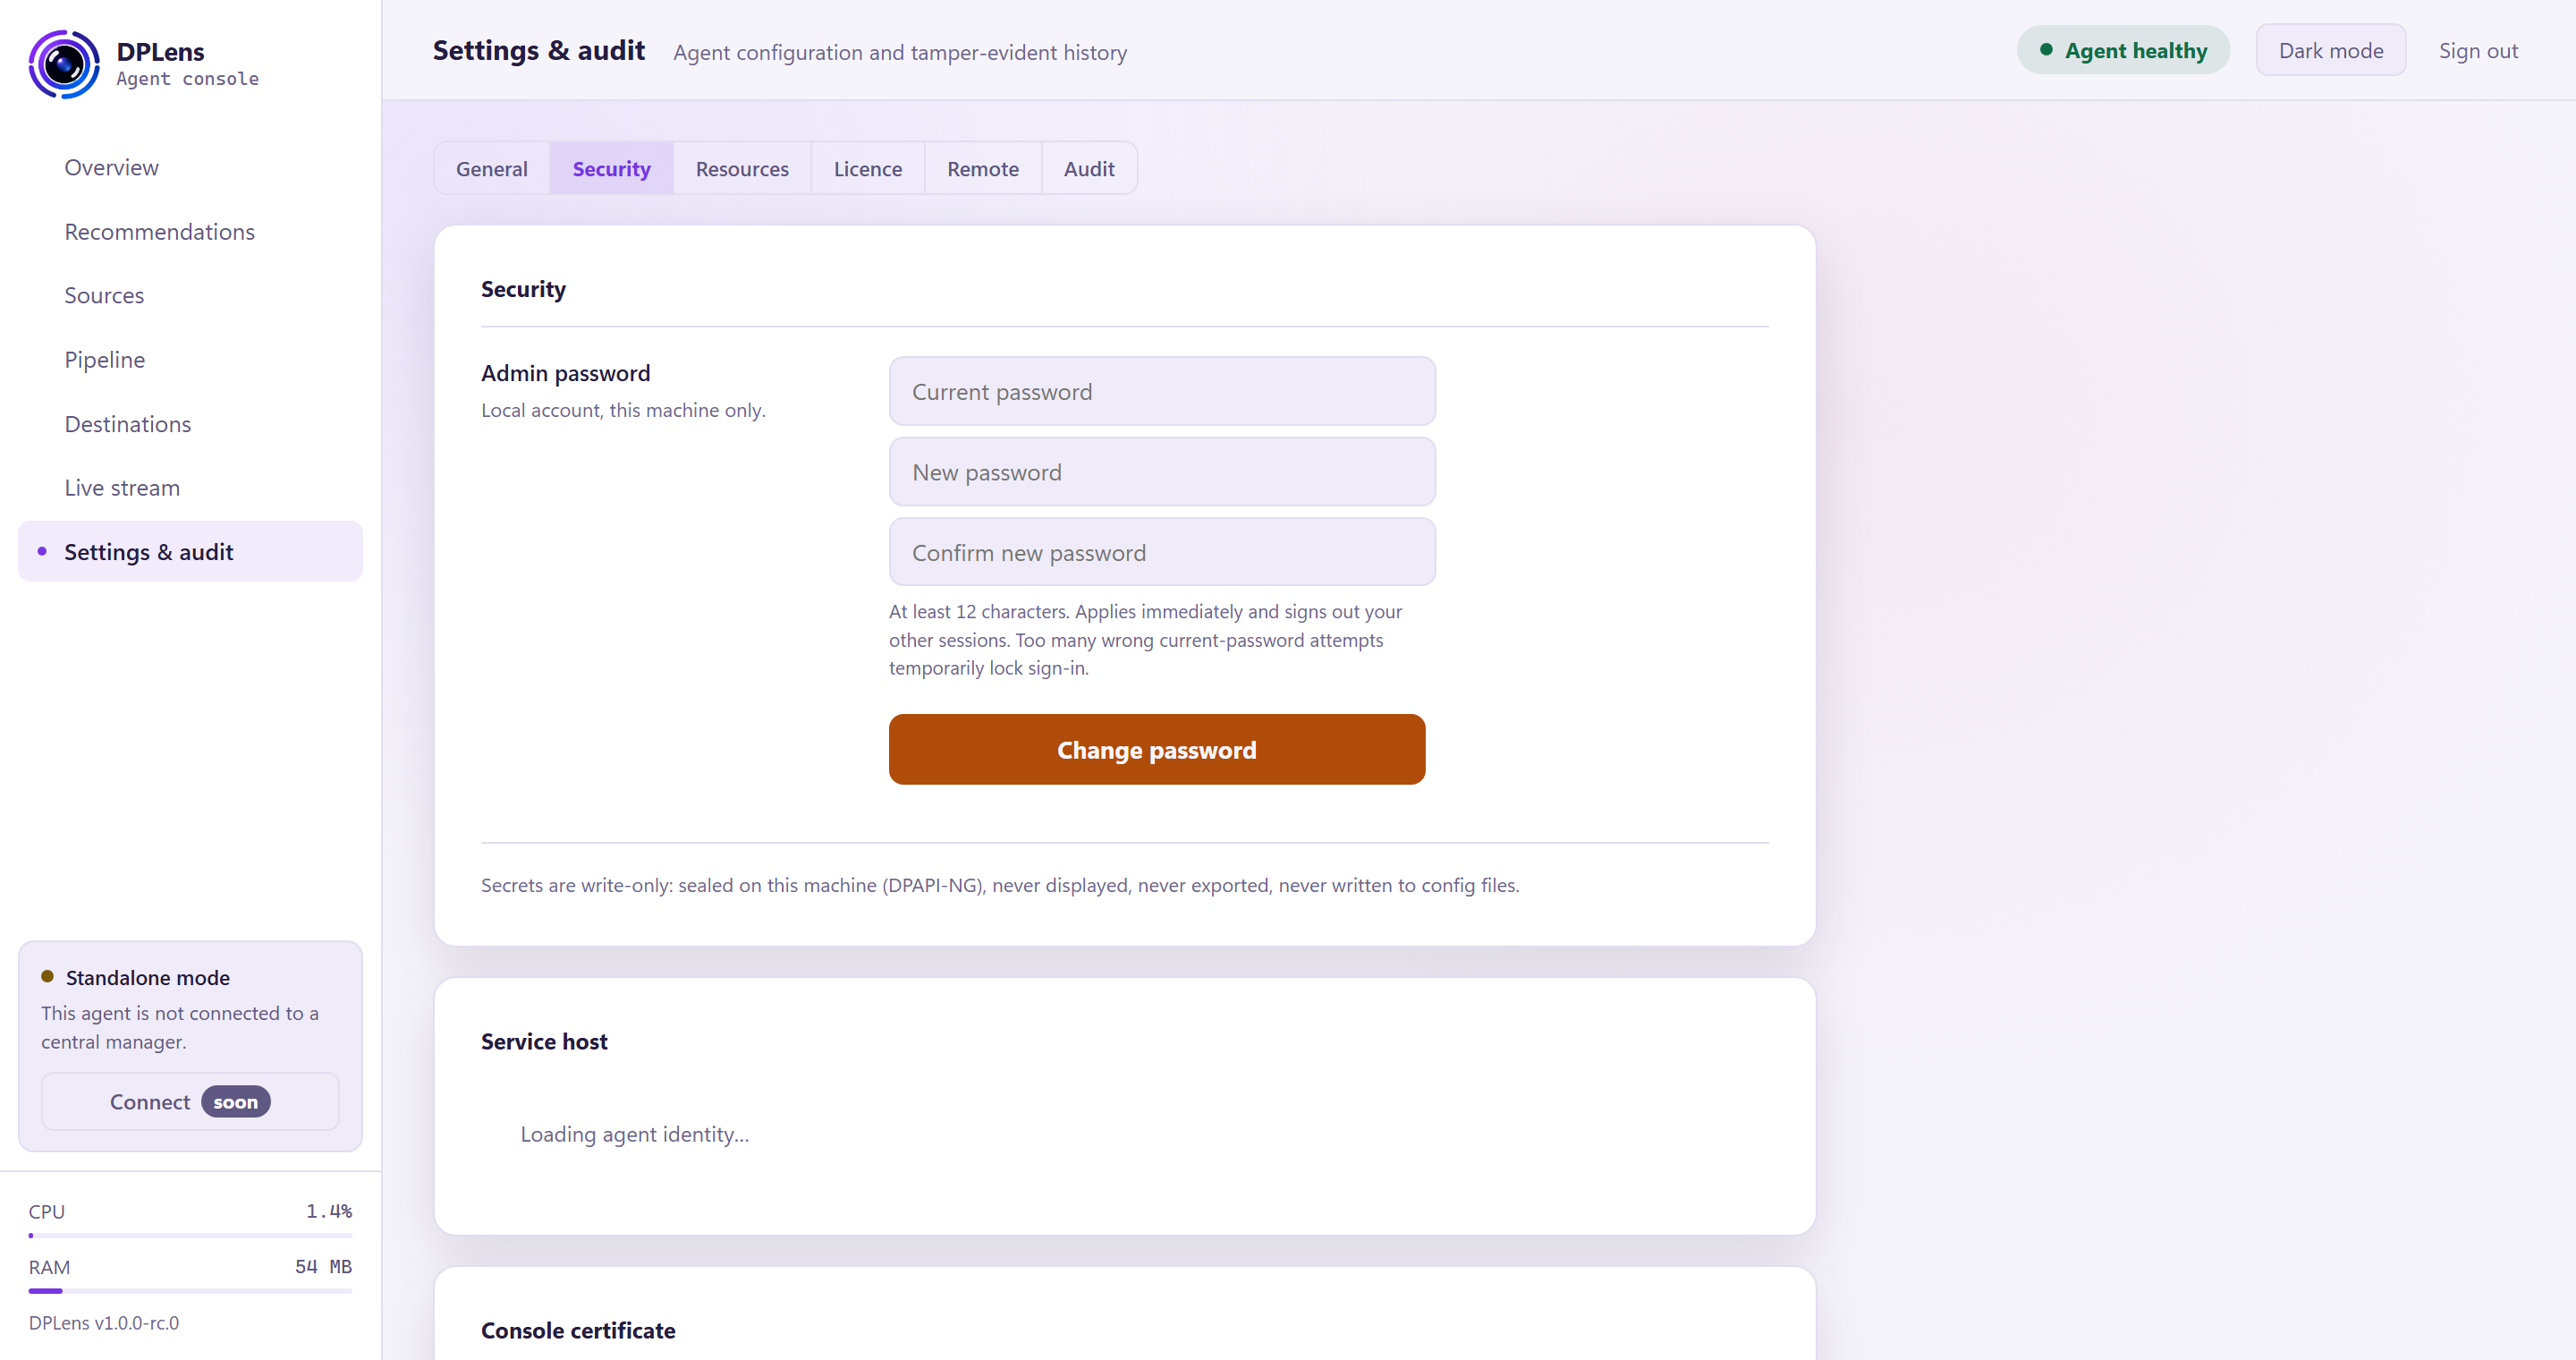
Admin password
Change the console password. Unlike everything else in the console this applies immediately — it is not staged — and it signs out your other sessions.
At least 12 characters. Repeated wrong guesses at the current password temporarily lock sign-in.
There is no recovery. The password is stored as a hash, and if it is lost an administrator on the machine sets a new one from the command line. The command reads the new password from its input rather than its command line, so it never appears in a command line or a process list. From an elevated Windows PowerShell prompt, stop the service, set the password, and start it again:
Stop-Service dplens
$exe = 'C:\Program Files\DPLens\dplens.exe'
$sec = Read-Host -AsSecureString 'New console admin password'
$psi = New-Object System.Diagnostics.ProcessStartInfo $exe, '--set-admin-password'
$psi.UseShellExecute = $false
$psi.RedirectStandardInput = $true
$p = [System.Diagnostics.Process]::Start($psi)
$b = [Runtime.InteropServices.Marshal]::SecureStringToBSTR($sec)
try {
  $bytes = [Text.Encoding]::UTF8.GetBytes([Runtime.InteropServices.Marshal]::PtrToStringBSTR($b))
  $p.StandardInput.BaseStream.Write($bytes, 0, $bytes.Length)
} finally { [Runtime.InteropServices.Marshal]::ZeroFreeBSTR($b) }
$p.StandardInput.Close(); $p.WaitForExit()
Start-Service dplens
The prompt hides what you type. The command prints dplens: admin password set when it succeeds.
The reset refuses to run while the service is running (exit code 5) and changes nothing: the running service is the only writer of the audit log, and a record written beside it would make the log fail its integrity check from then on.
Service host
How the collection service is running: which account it uses, whether the state folder's permissions are as they should be, and the machine identity the licence is bound to.
Console certificate
Install a certificate from your own authority so the console stops warning your browser. Paste the chain and the private key; the key is sealed on the machine and is never written to the configuration file, never displayed and never exported.
See Replacing the console certificate for the full procedure, including the headless route.
Secrets
The note on this tab is the rule the whole product follows: secrets are write-only. They are sealed to this machine, never displayed, never exported, never written to a configuration file. You can set one and see that a handle is in use; nothing can show you what is behind it, including the console itself.
Resources
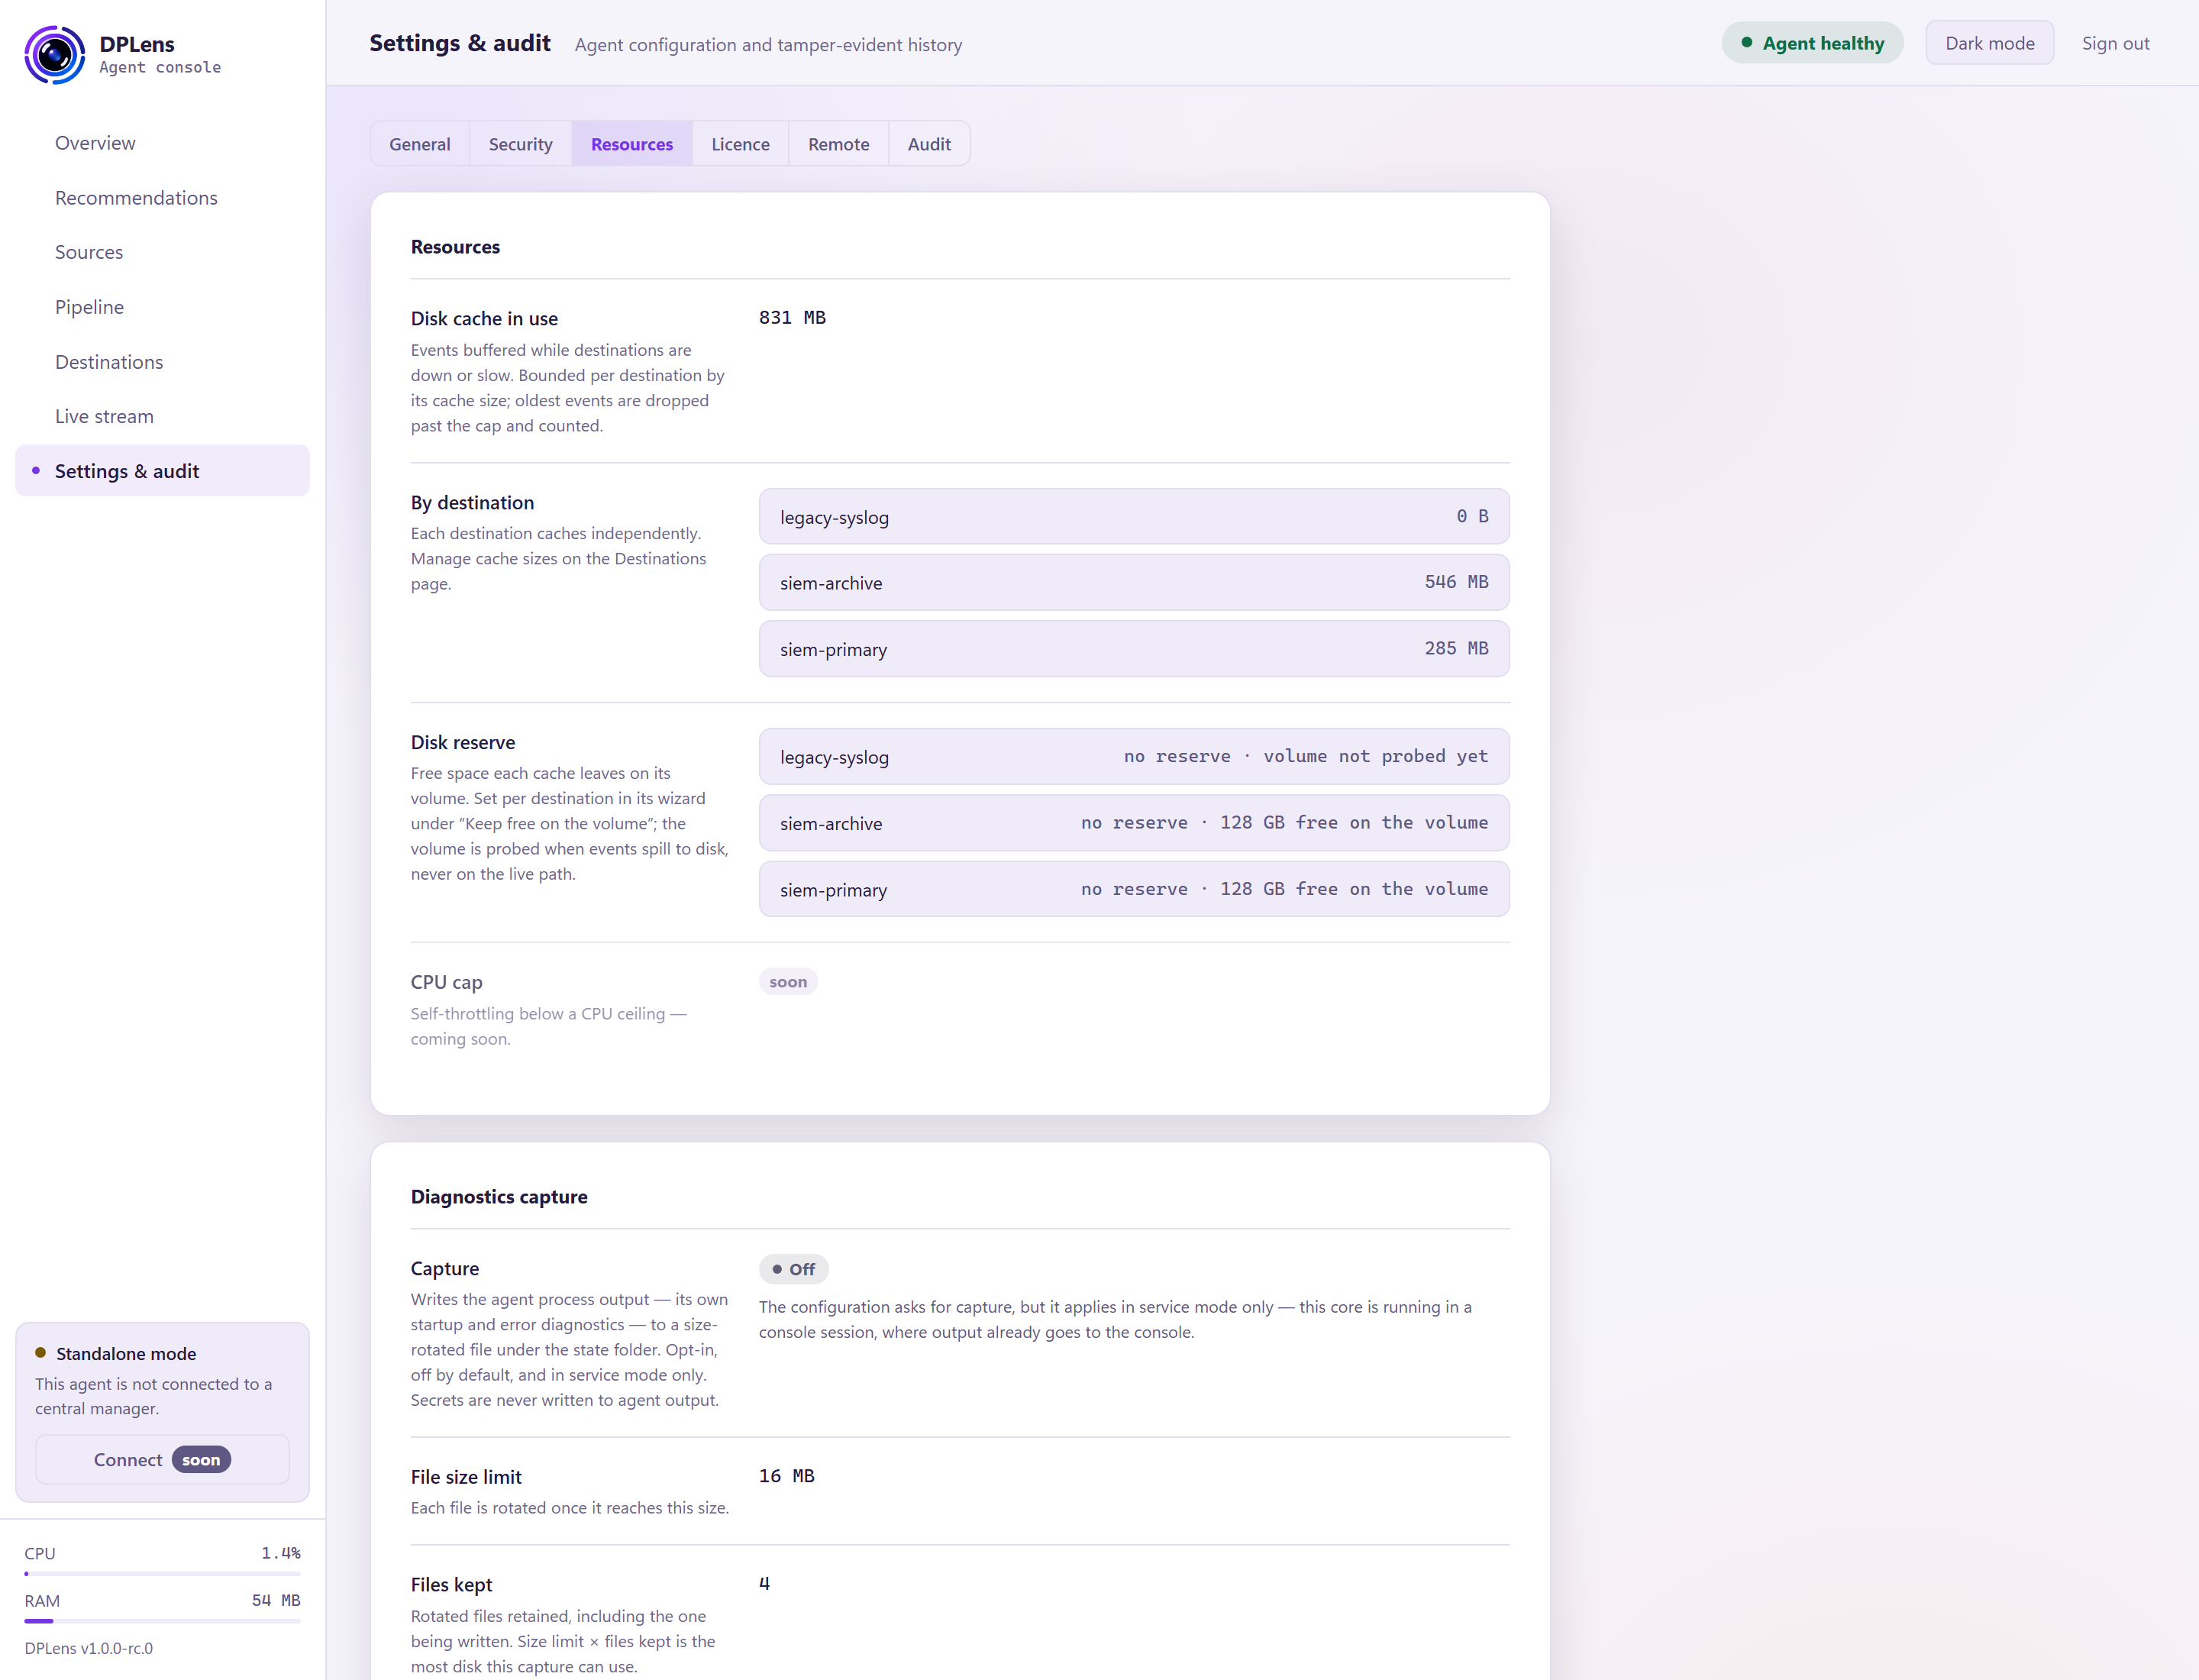
Read-only, except for the diagnostics settings.
Disk cache
How much is queued on disk in total, and per destination. Cache sizes are set per destination in its wizard — see Destinations.
Disk reserve
The free space each cache leaves on its volume. The volume is checked when events spill to disk, never on the live delivery path, so the check cannot slow down normal operation.
Memory backstop
A fixed safety limit, not a setting — there is nothing to change on this card.
Windows holds the agent's core process — the one that collects, processes and delivers your events — to a hard memory limit, so that nothing can make the agent take an ever-growing share of the machine.
| Field | |
|---|---|
| Status | In force, or Not in force with the reason. If the limit cannot be set up when the service starts, the agent runs anyway, says why here, and records it in the audit log. |
| Hard limit | 2 GB for the core process. The console and remote-management processes run under their own, smaller limits. |
| Early warning | 1 GB, counted across the core and the processes it launches. See below. |
| Core memory committed | How much the core process is using now, and its peak since it started. |
| Warnings | Appears once there has been one: how many times the early warning has fired since the service started. |
| Setup failures | Appears once there has been one: parts of the limit that could not be set up at start. |
The early warning is a signal, not a fault. When memory use crosses it, a warning is written to the audit log with how much was in use; nothing stops and nothing is dropped. It arms again once use has fallen well below the threshold, and fires at most once every five minutes, so it cannot flood the log. A common cause is events held in memory behind a slow or stalled destination — check the destination cards first.
If the hard limit is ever reached, the core process ends and the Windows service restarts it automatically — after 1, 5 and 30 seconds; a fourth failure within 24 hours leaves the service stopped until an administrator starts it. Events read from Windows event logs and log files are picked up again from where the agent left off. Events received over the network (syslog, NetFlow) that were still in memory are lost. The next start records in the audit log that the previous run did not stop cleanly.
The limit sits well above what a normally running agent uses. It is a backstop, not a target, and there is no setting for it.
Diagnostics capture
The agent's own startup and error diagnostics, written to a rotating file under the state folder.
| Setting | What it does |
|---|---|
| Capture | On or off. Off by default. |
| File size limit | The size at which the file rotates. |
| Files kept | How many rotations to keep, including the one being written. |
Size limit × files kept is the most disk this can ever use.
This is the agent talking about itself — not your log data. Secrets are never written to it. It applies when DPLens runs as a Windows service; run from a console, the output goes to the console instead.
Turn it on when you are investigating a problem, and off again afterwards. See Logs and health.
Licence
What your licence covers and when it expires. It never shows the key itself.
| Field | What it tells you |
|---|---|
| State | Licensed, in warning, in grace, or stopped |
| Data plane | Whether events are actually flowing under this licence |
| Customer | The organisation the key was issued to |
| Licence id | Unique to the issued key |
| Expiry | The date, and how many days remain |
| Agent entitlement | Whether local sources — Windows Event Log, file tail, file integrity — are covered |
| Receiver seats | Syslog and NetFlow receiver seats used against those available |
| Locked to | The machine or domain this key is valid for |
Below it, Apply a licence key: paste the key — one line, beginning DPL1 — and save.
A receiver seat is counted per configured, enabled receiver source, never per remote sender. A paused receiver holds no seat.
On an agent managed by DPLens Manager the page reports the lease the Manager granted, and applying a key is refused while the lease is held.
See Licensing.
Remote
Whether this agent is connected to a DPLens Manager, and how that connection stands. The tab is read-only: enrolment is done at install or with dplens.exe --enrol on the machine — see Enrolling an agent with DPLens Manager.
On a standalone agent the tab says so, and nothing on it does anything: the agent has no Manager connection at all.
On an agent set up for a Manager it shows:
| Field | What it tells you |
|---|---|
| State | unmanaged, enrolling, pending (waiting for approval), awaiting_seat (waiting for a licence seat), active, detaching, or refused (the Manager settings on this machine are unusable) |
| Manager | The Manager host the agent was set up with |
| Agent ID | A short digest of the identifier the Manager assigned |
| Identity key | Where the agent's identity key is held: in the machine's security hardware, or software_nonexportable for Windows' software key storage |
| Encryption key | Where the key that Manager-delivered secrets are encrypted to is held, the same way |
| Last check-in | When the agent last reached the Manager |
| Next check-in | When it will next try |
| Last code | The most recent outcome, by name |
| Alert | A condition that stops enrolment or check-in until you resolve it |
| Pin state | Which Manager certificate pin the last connection proved |
| Refusals | Setup refusals, token refusals and missing-token waits since the service started |
The note above the fields says whether the agent is managed. While it is, the sidebar reads Managed by your Manager, and the changes the Manager now owns are refused on every page — see What changes when an agent is managed.
Audit
A tamper-evident record of every change: what changed, when, and which account made it.
Each entry is chained to the one before it with a cryptographic hash, so a record cannot be altered or removed without breaking the chain. The agent also keeps a protected marker of the newest entry — the head anchor — so cutting entries off the end of the log, or putting an older copy back, is caught too.
| Column | |
|---|---|
| Time (UTC) | When it happened |
| User | The console account, or system for the agent's own actions |
| Change | What was done |
| Detail | The specifics |
How the log is checked
The agent checks the whole log when the service starts, and keeps checking it while it runs:
- Every time this page loads entries, each entry it shows is checked against the newest entry the agent wrote.
- In the background, the agent re-reads the whole log from the beginning, a little at a time, so a change far back in the history is found without a restart. A full pass takes about ten seconds per megabyte of log — a few minutes for a large one.
The status at the top of the list shows the result: Chain verified, or Integrity check failed.
When the check fails
A red banner appears above the entries, with the reason the agent found — for example, an entry that no longer matches its hash, entries missing from the beginning or the end of the log, or the protected marker not being saved. Nothing is hidden: every entry the agent can still read is listed, and an entry that cannot be tied to the verified history is marked unverified in the Change column. Treat those entries as suspect, and compare them with the copy delivered to your SIEM, if you ship one.
Once raised, the warning stays until the service next restarts, even if the cause has gone: a finding is evidence, and it is never cleared quietly. A restart checks the log again from scratch; if it now verifies, the warning clears. The detection is itself recorded in the log.
Head anchor save failures appears beside the status when the agent could not update its protected marker of the newest entry, with how many times that has happened since the service started. No entry is dropped and no action is refused: entries written meanwhile are still recorded and chained, but until the marker can be saved again they are not protected against being cut off the end. One cause is another program holding the marker file open — a backup, antivirus or monitoring tool reading the state folder.
The first failure of a run is recorded in the log, and that record is what lets the next start accept a marker left behind by it: the agent records that it accepted it, saves the marker, and starts clean. A marker more than one entry behind with no such record is treated as tampering.
After an upgrade from an earlier version, a machine where the marker had already stopped being updated shows the warning once, on the first start. The agent records it and saves the marker, and the next restart is clean.
Recorded here: sign-ins and failures, configuration applies and rollbacks, password changes, certificate installation, licence changes, masking policy changes, re-baselining a file-integrity source, and the agent's own start-up checks. The agent also records its own safety events: each early warning from the memory backstop, and any part of it that could not be set up at start; cached events that were removed from disk outside the agent — how many, and whether they were found missing while delivering from the cache or when the cache was reopened; and its checks of this log — a failed check and why, a failure to save the protected marker, and a start that found the marker behind and accepted it because the failure had been recorded.
The log is append-only and read-only. It cannot be edited or cleared from the console. It lives at C:\ProgramData\DPLens\state\audit\audit.jsonl — back it up with the rest of your state, and ship it to your SIEM if you want it retained centrally.